New - NVIDIA B200 & B300 Dedicated GPU Clusters | Explore GPU clusters
How to configure load balancing using Nginx
-
About
- Type
- Tutorial
- Categories
- Load balancingNetworking
Updated on 23.4.2026
Advantages of load balancing
Load balancing is an excellent way to scale out your application and increase its performance and redundancy. Nginx, a popular web server software, can be configured as a simple yet powerful load balancer to improve your server’s resource availability and efficiency.
How does Nginx work? Nginx creates a single entry point for a distributed web application that works on multiple servers.
This guide describes the advantages of load balancing. Learn how to set up load balancing with nginx for your cloud servers.
As a prerequisite, you’ll need to have at least two hosts with web server software installed and configured to see the benefit of the load balancer. If you already have one web host set up, duplicate it by creating a custom image and deploying it onto a new server at your UpCloud Control Panel.

Installing nginx
The first thing to do is set up a new host to serve as your load balancer. Deploy a new instance at your UpCloud Control Panel if you haven’t already. Nginx packages are available in the latest versions of CentOS, Debian, and Ubuntu. So pick whichever of these you prefer.
After setting up the server how you like, install the latest stable nginx. Use one of the following methods.
# Debian and Ubuntu
sudo apt-get update
# Then install the Nginx Open Source edition
sudo apt-get install nginx
# CentOS
# Install the extra packages repository
sudo yum install epel-release
# Update the repositories and install Nginx
sudo yum update
sudo yum install nginx
Once installed, change the directory to the nginx main configuration folder.
cd /etc/nginx/
Depending on your OS, the web server configuration files will be in one of two places.
Ubuntu and Debian follow a rule for storing virtual host files in /etc/nginx/sites-available/, which are enabled through symbolic links to /etc/nginx/sites-enabled/. You can use the command below to enable any new virtual host files.
sudo ln -s /etc/nginx/sites-available/vhost /etc/nginx/sites-enabled/vhost
CentOS users can find their host configuration files under /etc/nginx/conf.d/ in which any .conf type virtual host file gets loaded.
Check that you find at least the default configuration, and then restart nginx.
sudo systemctl restart nginx
Test that the server replies to HTTP requests. Open the load balancer server’s public IP address in your web browser. When you see the default welcoming page for nginx, the installation is successful.
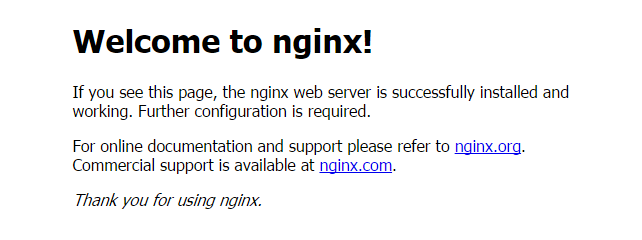
If you have trouble loading the page, check that a firewall is not blocking your connection. For example on CentOS 7 the default firewall rules do not allow HTTP traffic, enable it with the commands below.
sudo firewall-cmd --add-service=http --permanent
sudo firewall-cmd --reload
Then, try reloading your browser.
Configuring nginx as a load balancer
When nginx is installed and tested, start to configure it for load balancing. In essence, all you need to do is set up Nginx with instructions on which type of connections to listen to and where to redirect them. Create a new configuration file using whichever text editor you prefer. For example, with nano:
sudo nano /etc/nginx/conf.d/load-balancer.conf
In the load-balancer.conf, you’ll need to define the following two segments: upstream and server. See the examples below.
# Define which servers to include in the load balancing scheme.
# It's best to use the servers' private IPs for better performance and security.
# You can find the private IPs at your UpCloud control panel Network section.
http {
   upstream backend {
      server 10.1.0.101;
      server 10.1.0.102;
      server 10.1.0.103;
   }

   # This server accepts all traffic to port 80 and passes it to the upstream.
   # Notice that the upstream name and the proxy_pass need to match.

   server {
      listen 80;

      location / {
          proxy_pass http://backend;
      }
   }
}
Then, save the file and exit the editor.
Next, disable the default server configuration you tested earlier that was working after the installation. Again, this part differs slightly depending on your OS.
On Debian and Ubuntu systems, you’ll need to remove the default symbolic link from the sites-enabled folder.
sudo rm /etc/nginx/sites-enabled/default
CentOS hosts don’t use the same linking. Instead, simply rename the default.conf in the conf.d/ directory to something that doesn’t end with .conf, for example:
sudo mv /etc/nginx/conf.d/default.conf /etc/nginx/conf.d/default.conf.disabled
Then, use the following to restart nginx.
sudo systemctl restart nginx
Check that nginx starts successfully. If the restart fails, take a look at the /etc/nginx/conf.d/load-balancer.conf you just created to make sure there are no mistypes or missing semicolons.
When you enter the load balancer’s public IP address in your web browser, you should pass it to one of your back-end servers.
Load balancing methods
Load balancing with nginx uses a round-robin algorithm by default if no other method is defined, like in the first example above. With a round-robin scheme, each server is selected in turns according to the order you set them in the load-balancer.conf file. This balances the number of requests equally for short operations.
Least connections-based load balancing is another straightforward method. As the name suggests, this method directs the requests to the server with the least active connections at that time. It works more fairly than round-robin with applications where requests sometimes take longer to complete.
Add the parameter least_conn to your upstream section to enable the least connections balancing method, as shown in the example below.
upstream backend {
   least_conn;
   server 10.1.0.101;
   server 10.1.0.102;
   server 10.1.0.103;
}
Round-robin and least connections balancing schemes are fair and have their uses. However, they cannot provide session persistence. If your web application requires that the users are subsequently directed to the same back-end server as during their previous connection, use the IP hashing method instead. IP hashing uses the visitor’s IP address to determine which host should be selected to service the request. This allows the visitors to be directed to the same server each time, granted that the server is available and the visitor’s IP address hasn’t changed.
To use this method, add the ip_hash -parameter to your upstream segment, as in the example below.
upstream backend {
   ip_hash;
   server 10.1.0.101;
   server 10.1.0.102;
   server 10.1.0.103;
}
In a server setup where the available resources between different hosts are unequal, favouring some servers over others might be desirable. Defining server weights allows you to fine-tune the load and further balance it with nginx. The server with the highest weight in the load balancer is selected the most often.
upstream backend {
   server 10.1.0.101 weight=4;
   server 10.1.0.102 weight=2;
   server 10.1.0.103;
}
For example, in the configuration shown above, the first server is selected twice as often as the second, which again gets twice the requests compared to the third.
Load balancing with HTTPS enabled
Enable HTTPS for your site; it is a great way to protect your visitors and their data. If you haven’t yet implemented encryption on your web hosts, we highly recommend you look at our guide for installingLet’s Encrypt on nginx.
Using encryption with a load balancer is easier than you might think. All you need to do is add another server section to your load balancer configuration file that listens to HTTPS traffic at port 443 with SSL. Then, set up a proxy_pass to your upstream segment, like with the HTTP in the previous example above.
Open your configuration file again for editing.
sudo nano /etc/nginx/conf.d/load-balancer.conf
Then, add the following server segment to the end of the file.
server {
   listen 443 ssl;
   server_name domain_name;
   ssl_certificate /etc/letsencrypt/live/domain_name/cert.pem;
   ssl_certificate_key /etc/letsencrypt/live/domain_name/privkey.pem;
   ssl_protocols TLSv1 TLSv1.1 TLSv1.2;

   location / {
      proxy_pass http://backend;
   }
}
Then, save the file, exit the editor, and restart Nginx.
sudo systemctl restart nginx
Setting up encryption at your load balancer when you are using private network connections to your back end has some great advantages.
- As only your UpCloud servers have access to your private network, you can terminate the SSL at the load balancer and thus only pass forward HTTP connections.
- It also greatly simplifies your certificate management. You can obtain and renew the certificates from a single host.
With the HTTPS-enabled, you can enforce encryption on all connections to your load balancer. Simply update your server segment by listening to port 80 with a server name and a redirection to your HTTPS port. Then, remove or comment out the location portion as it’s no longer needed. See the example below.
server {
   listen 80;
   server_name domain_name;
   return 301 https://$server_name$request_uri;

   #location / {
   #   proxy_pass http://backend;
   #}
}
Save the file again after you have made the changes. Then restart nginx.
sudo systemctl restart nginx
Now, all connections to your load balancer will be served over an encrypted HTTPS connection. Requests to the unencrypted HTTP will be redirected to use HTTPS as well. This provides a seamless transition into encryption. Nothing is required from your visitors.
Health checks
Nginx’s reverse proxy implementations include passive server health checks to determine which servers are available. If a server fails to respond to a request or replies with an error, nginx will note that it has failed and try to avoid forwarding connections to that server for a time.
The number of consecutive unsuccessful connection attempts within a certain time period can be defined in the load balancer configuration file. Set a parameter max_fails to the server lines. By default, when no max_fails is specified, this value is set to 1. Optionally, setting max_fails to 0 will disable health checks for that server.
If max_fails is set to a value greater than 1, subsequent fails must happen within a specific time frame for them to count. This time frame is specified by a parameter, fail_timeout, which also defines how long the server should be considered failed. By default, the fail_timeout is set to 10 seconds.
After a server is marked failed and the time set by fail_timeout has passed, nginx will begin gracefully probing the server with client requests. If the probes return successful, the server is again marked live and included in the load balancing as normal.
upstream backend {
   server 10.1.0.101 weight=5;
   server 10.1.0.102 max_fails=3 fail_timeout=30s;
   server 10.1.0.103;
}
Use the health checks. They allow you to adapt your server back-end to the current demand by powering up or down hosts as required. Adding more servers during high traffic can easily increase your application performance as new resources become automatically available to your load balancer.
Conclusions on the advantages of load balancing
If you wish to improve your web application performance and availability, a load balancer is definitely something to consider. Nginx is powerful yet relatively simple to set up to load balance a web server. Together with an easy encryption solution, such as the Let’s Encrypt client, it makes for a great front-end to your web farm. Check out the documentation for upstream over at nginx.org to learn more.
When you use multiple hosts, the load balancer protects your web service with redundancy, but the load balancer itself can still leave a single point of failure. You can improve high availability by setting up a floating IP between multiple load balancers. Check out our article about floating IPs on UpCloud to learn more.
Ash
This article saved my butt, thank you. Very clear and helpful.
Adi
Nice article!
Thanks!
Amit
Nice article!
Thanks!
pradeep
good document
Felix
Thanks for your awesome documentation ! What is the best between having a nginx load balancer plus integrated swarm load balancer or using round robin dns?
Agung
i don’t have load balance config in my nginx ?
Turan
You are great!
Waleed Khan
Hi Janne,
Great article thanks. I just have a question. I am converting my current single Nginx configuration to a frond end proxy with multiple back end servers like you stated above.
What I am not sure about is what to put on the back end servers and how to configure Nginx on those servers.
The front end server has the content and the SSL certs configured on it but to get the benefit of the load balancing, what data and Nginx configs needs to sit on the back end servers i.e. server 10.1.0.101, , 10.1.0.102, 101.1.0.103 in your cluster?
Thanks.
Serkan Coskun
Thanks!!
A
Looking at above diagram image, what if the Load Balancer machine is down?
Yan
Justt put the Load Balancer in HA with DNS, two load balancer or just use router
Hieu Doan
Great Article! Thank you so much! Keep your awesome work.
JOHN Maina Kamau
Great article. Very well done.
Arun Nadesh
Excellent article which covers everything developers wants to know to use nginx as load balancer.Thanks Much!
Harvey Jones
Thanks for the article. I found Nginx very helpful but I wan’t always this sure I had my doubts.
Ashutosh
Hii.. we have setup a load balancer with 2 servers. We are facing issues while streaming and playing back the same video. If the request is going to one of the servers suppose S1 and for playback the request is going to the server S2 ,in that case we are not able to playback the video. And since we are using the load balancer we can have the request on any of the servers irrespective on which the LB decides.
So can we have any ways where we can have the the publish and play request going to the same server through the LB.
Ganesh Arelly
Hello Janne,
Clear explanation, nice write-up.
We are a start-up from Finland. Horizontal scaling is not an option with us for some legacy software licensing costs. However, we can deploy two application servers at different ports on the same node.
So, Is it possible load balance on same node between two ports? Something like:
upstream backend {
server 10.1.0.101:7777;
server 10.1.0.101:7778;
}
Reply
Janne Ruostemaa
Hi Ganesh, thanks for the question. Indeed it is possible to set the backend as you described, however, you won’t get the same benefits of redundancy and scalability by deploying multiple instances of your application on the same server.
Nwanze Franklin
Nice article. very helpful
Samrat
great article to get start with Nginx.
Kashish
Hello Janne,
Nice explanation.
I have a question: Is it possible to do load balancing in such a way that all the request with same cookie value goes to the same instance ?
Janne Ruostemaa
Hi Kashish, thanks for the question. Nginx does support session persistence using cookies but it’s only available in Nginx Plus. Alternatively, you could use the IP hash method to ensure that requests from the same address get to the same server.
Harish N J
Hi Janne,
I am seeing an unexpected behaviour with nginx, when used as a udp load balancer.
My client and server is supposed to exchange udp packets back and forth between them for longer period. My server will be listening to a specific port and the client will initate the communication with a random port and continue to use it for all communication with the server.
When i try to introduce NGINX in this topology to proxy the packets, i could see that after few seconds. NGINX changes the port number, which it used to communicate with the backend server for the same client. Hence the server losses the context of the session and thereby resulting in connection loss.
This behaviour is consistent across both nginx & nginx plus.
I have tried proxy_timeout option as well, which doesn’t solves the purpose.
Is it a known issue of nginx ?
eleman
This article is gonna save our butts as a startup
Mike
I’m a bit confused on this. I’m running on CentOS and I never had a default.conf file in my conf.d directory.
When I create my loadbalancer.conf and try and restart nginx I get some errors around the following –
nginx: [emerg] “http” directive is not allowed here in /etc/nginx/conf.d/loadbalancer.conf:1
There are some other guides that are telling me to put what you have in loadbalancer.conf into my actual nginx.conf but that also is not working.. I’ve started fresh dozens of times and not sure what i’m doing wrong here.
I get my initial nginx welcome page but as soon as I add the loadbalancer.conf and reload it fails to start.
Nigel
With this method, the server logs always show the load balancer IP not the connecting client IP.
I’ve tried adding “proxy_bind $remote_addr transparent;” and “user root; ” but I’m getting timeouts when the option is enabled.
I’m wondering if this feature has been pulled and now only available in the Nginx plus version, or have I missed something that is required to make it work?
Kate
so i just start learning about load balancing.
if i have php on the backend, shoud i install php fpm on load balancer server, or all process is done in the backend?
Mohamad
Thanks for your Article
I need some help about this challenge:
Setup 2 separate PHP-FPM Servers and configure Nginx to balance the load between them.
+ Requests to WordPress admin must be sent to just one of them
+ PHP-FPM workers should run under the user you have created
* I have created a pool named user1 , but i don’t know what should I do? because i have to implement it on one server
Joel Alvarado
Awesome article Janne.
Could you please help me with something. I did all the steps for load balance two php sites in two different servers, the two sites are using nginx as web service too, and it works really nice, the challenges begin when I decide to migrate those two servers from http to https. On http it works very easy and very good, but when those servers start working on ssl, it becomes all just a mess up. If I set the dns domain and point to one server only, it works fine, http redirects to https and IP requests redirects to dns requests, I tried this on boths servers 1 by 1 separate, and it works. But in https load balance mode, the best thing I get, is load balance the default nginx site on those servers, it does the balance but shows the default nginx site, not my app site, if I try to unlink the default site, only shows 404 not found, no redirect to the app. I used certbot to set ssl in both servers, I tried to set the load balancer with and without ssl certificates, with certbot too, But I can never make it work Well. Question, my servers need to be ssl or not? Could you please help me to complete this task?
Bibek Gupta
One of the best article you could ever find on load balancer with NGINX. Great article!
Adi
You save my day! Maybe my whole year! :D
I’ve got this headache for the load of my server. Thank you in millions.
Kai
Thanks you for this great article Janne
I need a note for following question. We run nginx as reverse proxy, 3 upstream server, ip_has method, proxy_cache_key is “$scheme$request_method$host$request_uri$cookie_NAME.
Caching works fine. But in case that a user visit one website and come later to the same site, but with active authcookie, nginx deliver the cached site. But is necessary to generate a new one, because some content is changed. Can nginx do that?
Kai
Hallo Janne,
thanks for help, proxy_cache_bypass and proxy_no_cache works fine for me.
Kind regards, Kai
Shoaib
Hey, Great article
Would it be possible to add another backend server on the fly without having to restart the load balancer (in scaling out use case). Any offline method/software/framework to auto scale and dynamically load balance on a private network
Thanks
Raju
I have server configuration like http://localhost:8080/abc/xyz.com , here where we need give this context path
Valcenir
Very nice article!
Thanks!
sravya
Hi Jaane
Great article. I have some doubts.
How much size of db is required for nginx to store data and suppose if install nginx in linux can we add windows in conf file or do we need to make changes in conf as per windows
Oscar
Hi Janne, great article.
Which services combinations are allowed to use in nginx at the same time? I mean it’s possible to use as a load balancer and as a web server and as a reverse proxy at the same time? Thnx
Vong Ho
This is very useful article. Tks a lot
Spencer
hi, thanks for a great tutorial, can you please assist with my setup? I hav ethe following nginx.conf:
`
# declare flask app
upstream pyapi_app {
least_conn;
server pyapi1:5000;
server pyapi2:5000;
}
# declare shiny app
upstream shiny_app {
server shinyapp:3838;
}
map $http_upgrade $connection_upgrade {
default upgrade;
” close;
}
# shinyapp server
server {
listen 80 default_server;
server_name shiny_app;
client_max_body_size 50M;
# normal requests go to shiny app
location / {
proxy_pass http://shiny_app;
proxy_redirect off;
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Host $server_name;
proxy_http_version 1.1;
proxy_set_header Upgrade $http_upgrade;
proxy_set_header Connection $connection_upgrade;
proxy_read_timeout 5d;
proxy_buffering off;
}
}
# python api server
server {
listen 81;
server_name pyapi_app;
# pyapi requests go to the flask app
location / {
proxy_pass http://pyapi_app;
proxy_redirect off;
proxy_set_header Host $host;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header X-Forwarded-For $proxy_add_x_forwarded_for;
proxy_set_header X-Forwarded-Host $server_name;
}
}
`
what do I put in my shinyapp frontend in regards to the URL connection string? Prior to scaling up the api backend, I just put the name of the docker container or the ip address of the pyapi server, `pyapi:5000/post` but now that I have 2x `pyapi`s how should I write it?
Gebriel
No word! it helps me a lot! Thank you soooooooooooooooooooooo muchhhhh !!
Ashok
What about load balancing with Litespeed server?
Sean
Good stuff, thank you. I was having problems with the load-balancer.conf file because both that and the nginx.conf included http {}. I had to remove that from my load-balancer.conf file before I could get nginx to restart successfully.
Prasad
Excellent Article! Thanks for such a detailed article. It helped save a lot of time and effort!
D
Hi, thanks for the info. Will this configuration work if I don’t have a dedicated load balancing server? I’m trying to configure nginx on one of the three syslog servers I want to load balance between.
D
Thanks, I’m really new to this so you’ve been a big help. One more question: when you say “When you enter the load balancer’s public IP address in your web browser, you should pass to one of your back-end servers,” how do I know if it passed to a back-end server?
Devesh Sharma
Hi! That was very informative article.
Just want to know how should I pass the upstream, location and proxy_pass such that if I type docker3_ip/apache-docker1, apache webserver from docker 1 opens. Similarly, if I type docker3_ip/apache-docker2, apache webserver from docker 2 opens and if I type docker3_ip/apache it should send equal no of alternate request to one another.
Le Bach
Hello Janne!
Here is the contents of my mydomainxyz.com.conf file: https://products.groupdocs.app/viewer/view?file=dc46056e-78c4-4ea3-ad54-211e4801336a/file.txt
Currently my origin server is in US. I cloned using the “Clone” feature adding 2 more regions: Singapore & Germany. and i have 3 servers. I have some questions as follows:
– Do I have to upload load-balancer.conf to the origin server, or all 3 servers?
– How can customers near Singapore area automatically get the nearest server?
– with my mydomainxyz.com.conf file, how do I set up to get the complete load-balancer.conf file? i’m bewildered because i don’t understand anything about nginx.
Looking forward to help!
Abdullahi
Hi Janne,
Trust this meets you well
You are simply the best…please i need your advise and clarification on setting up four primary web servers(JBoss) on Primary DMZ and another four secondary web servers(JBoss) on secondary DMZ. The question is how do i setup NGNIX load balancer to automatically failover to the seconday DMZ if there is completely outage on Primary DMZ.
Vasudevan Rao
Hello UpCloud
It was indeed an excellent article on how to proceed with nginx right from the installation till configuring “nginx” as a load balancer. I am using Mac OSX that I installed through Homebrew. Very much useful for any person understanding on load balancer. You have done a excellent, fantastic and awesome job guiding others in this aspect. I really apprecaite from the bottom of my heart. Thanks indeed
Josh Weinthraub
Is it possible to use Cloudflare with NGINX load balancer?
Munir
Hi, thanks for this article.
I have a question that if there’s only one baremetal node where web server is hosting multiple static web pages, how can they be load balanced on single server. Like different clients reuqesting different pages and load balancer is serving their respective resquests?
Arian Moafizad
Hello,
First of all thanks for the article. It is very assertive.
I configured my NGINX server as a load-balancer with health_check, but when I want to reload the NGINX, it says:
“nginx: [emerg] unknown directive “health_check” in /etc/nginx/conf.d/test.conf:15
nginx: configuration file /etc/nginx/nginx.conf test failed”
Here is my configuration from /etc/nginx/conf.d /test.conf:
upstream mylab {
server 192.168.56.11;
server 192.168.56.12;
zone mylab 64k;
}
server {
server_name mylab.local.net;
listen 80;
location / {
proxy_pass http://mylab;
proxy_set_header X-Real-IP $remote_addr;
proxy_set_header HOST $host;
health_check;
}
}
server {
server_name mylab.local.com;
listen 80;
location / {
proxy_pass http://mylab;
proxy_set_header X-Real_IP $remote_addr;
proxy_set_header HOST $host;
health_check;
}
}
I used CentOs 7.9 .
I’ll appreciate you if you could help me to solve the issue.
chase
this question is exactly what I came to this article for! thanks! great article!
lewis
very useful and simple… thanks!!
Amanullah Aman
Hi,
First of all, thank you for this nice tutorial about load balancing.
I have a little confusion. If anyone explains me, It would be very helpful to me.
upstream backend {
least_conn;
server 10.1.0.101;
server 10.1.0.102;
server 10.1.0.103;
}
In this example, there are 3 servers. That means the same application is running on 3 different servers. Now my question is On which server I will install and configure Nginx for load balancing? Is it on a completely separate server or anyone above example upstream backend server? If we need to install Nginx on a separate server then what will be this server configuration? Is it the same configuration as our upstream backend servers or less configured or more powerful?
Thanks.
Janne Ruostemaa
Hi Amanullah, thanks for the question. Ideally, you would install the load balancer, like in this tutorial, on one machine and all applications on separate backend servers. Commonly, the application servers need to be more powerful to handle the actual client requests but that is entirely dependent on the service you are hosting.
vcffile.com
very useful and simple tool…
said
weird i have this error:
http” directive is not allowed here in /etc/nginx/conf.d/load-balancer.conf
anybody had it?